The kitchen table sits quiet under the pale morning light while coffee brews in the corner. You glance at your smartphone resting on the wooden surface, expecting the usual steady trickle of morning work emails and group chat check-ins. Instead, the signal bars in the upper right corner quietly collapse into a stark, hollow icon that reads ‘SOS Only’ or ‘No Service.’ You toggle airplane mode, assuming a nearby cell tower hiccuped during routine maintenance. You restart the device. The glass stays cold, the cellular bars refuse to return, and within four minutes, your primary email account suddenly demands a password re-entry on your laptop.
That quiet vanishing of your cellular connection is not a carrier glitch. It is the precise sensory hallmark of a successful SIM swap attack. Miles away, an attacker has convinced a tired retail clerk at a cellular kiosk to redirect your phone number to a blank physical plastic card or a freshly generated eSIM profile. In seconds, every single digital boundary protecting your life dissolves, because decades of web architecture quietly built their most critical safety nets on top of an archaic telecommunications standard designed in the 1980s.
When a bad actor holds your telephone number, every vulnerable six-digit text code sent by your banking portal, your password manager recovery address, and your personal communications pipeline lands squarely in their palm. The green or blue bubbles you trusted to verify your identity were never designed to be security keys; they were designed to be digital postcards. Reclaiming control begins the moment you tear down that flimsy radio-frequency bridge and replace it with unyielding cryptographic hardware.
The Carrier Illusion: Why Text Messages Were Never Passwords
To grasp why text message verification fails, think of your cellular carrier not as a fortified vault, but as a suburban post office staffed by overworked seasonal workers. When you ask a digital service to verify your identity via SMS, you are essentially asking a stranger behind a retail counter in a strip mall to protect your entire life savings. Social engineering attacks do not target advanced mathematical ciphers; they target minimum-wage customer service reps who are systematically manipulated with fake badges, sob stories, or direct financial bribes to reassign telephone routing tables.
Once a telecom employee clicks ‘transfer’ on their customer relationship screen, your physical phone becomes an empty shell. The attacker does not need your fingerprint, your home WiFi network, or your complex alphanumeric password. They simply trigger account recovery prompts across your financial dashboard, catch the inbound text messages like dry leaves falling into a net, and lock you out of your digital existence before you can even locate your carrier’s customer support line.
Hardware authentication, embodied by YubiKey security keys, alters this dynamic by establishing a protocol of absolute physical presence. A security key does not negotiate with human customer service agents, nor does it rely on radio waves traveling through vulnerable cellular switches. It anchors your identity to an onboard cryptographic chip running Fast Identity Online (FIDO2) and WebAuthn standards, requiring an unforgeable physical touch that no rogue call-center staffer or foreign syndicate can mimic across a fiber optic cable.
- Apple AirPods Max stop choppy audio dropouts after resetting congested network caches
- OLED monitor screens stop gritty evening eye burn after shifting refresh rate toggles
- WhatsApp chat backups clog internal smartphone memory with endless bloated video clutter
- Wells Fargo alerts spoof urgent customer notifications hiding fake account reset traps
- Nothing Ear (a) earbuds silence loud commuter rumble matching luxury flagship sound
The Shift: Lessons from an Incident Responder
Consider the experience of Elena Ramos, a 42-year-old network systems analyst from Columbus, Ohio. In the autumn of 2023, Elena watched a client’s commercial account hemorrhage half a million dollars over a single weekend after an attacker sweet-talked an authorized retail worker into transferring a corporate executive’s phone number during an evening shift change. The attackers bypassed every layer of software protection precisely because the executive relied on text-message prompts for secondary authentication. Elena spent forty-eight sleepless hours rebuilding destroyed credentials, watching firsthand how an exploit occurring hundreds of miles away in an air-conditioned strip mall could vaporize an organization’s digital moat. That following Monday, she permanently stripped cellular numbers from every recovery profile across her client rosters and mandated physical hardware keys, cutting their attack surface to absolute zero.
Layering the Defenses: Tailoring Hardware Security to Your Life
Adopting physical authentication does not require a degree in computer engineering, but it does require understanding where you fit along the digital exposure spectrum. Not everyone handles corporate wire transfers, yet everyone holds valuable data that predatory brokers actively hunt.
For the Everyday Consumer: If your digital world revolves around personal banking, family photo libraries, and shopping accounts, your primary vulnerability lies in automated password resets. Setting up a dual-port USB-C and Lightning or NFC-enabled hardware key provides instant peace of mind. You plug it into your computer or tap it against the back of your smartphone whenever you sign in from a new browser. Without that physical tap, nobody enters—even if they possess your username, password, and cellular number.
For the High-Profile Professional or Independent Business Owner: If a compromised email account could compromise payroll, customer records, or client confidentiality, standard hardware key integration must extend beyond your email login. You must configure hardware-backed passkeys for your domain registrar, business accounting suites, and enterprise messaging boards. In this posture, you intentionally delete your phone number from every recovery field across Google, Apple, and your financial institutions, leaving physical cryptographic hardware as the sole authorization mechanism.
For the Multi-Device Family: Safeguarding a household requires removing points of failure without creating friction that drives family members back to unsafe habits. Modern hardware keys utilize Near Field Communication, allowing teenagers and non-technical spouses to authenticate logins by simply tapping the small polymer token against the top edge of an iPhone or Android device, eliminating the frustration of hunting for fleeting SMS codes in busy moments.
Mindful Application: The Zero-Trust Setup Guide
Transitioning from fragile text verifications to hardware tokens should be a calm, methodical process. Do not rush to reconfigure twenty accounts at once. Focus on your primary email address first, as it acts as the master key to everything else you own.
Begin by securing a pair of identical security keys. Never rely on a single physical token; having a designated primary key on your everyday keychain and a backup key stored in a fireproof home safe prevents accidental lockouts if you misplace your daily driver.
- Acquire two hardware keys supporting modern FIDO2 and WebAuthn protocols (such as a YubiKey 5 Series).
- Log in to your master email account (Google, Proton, or Apple ID) and navigate to the security settings.
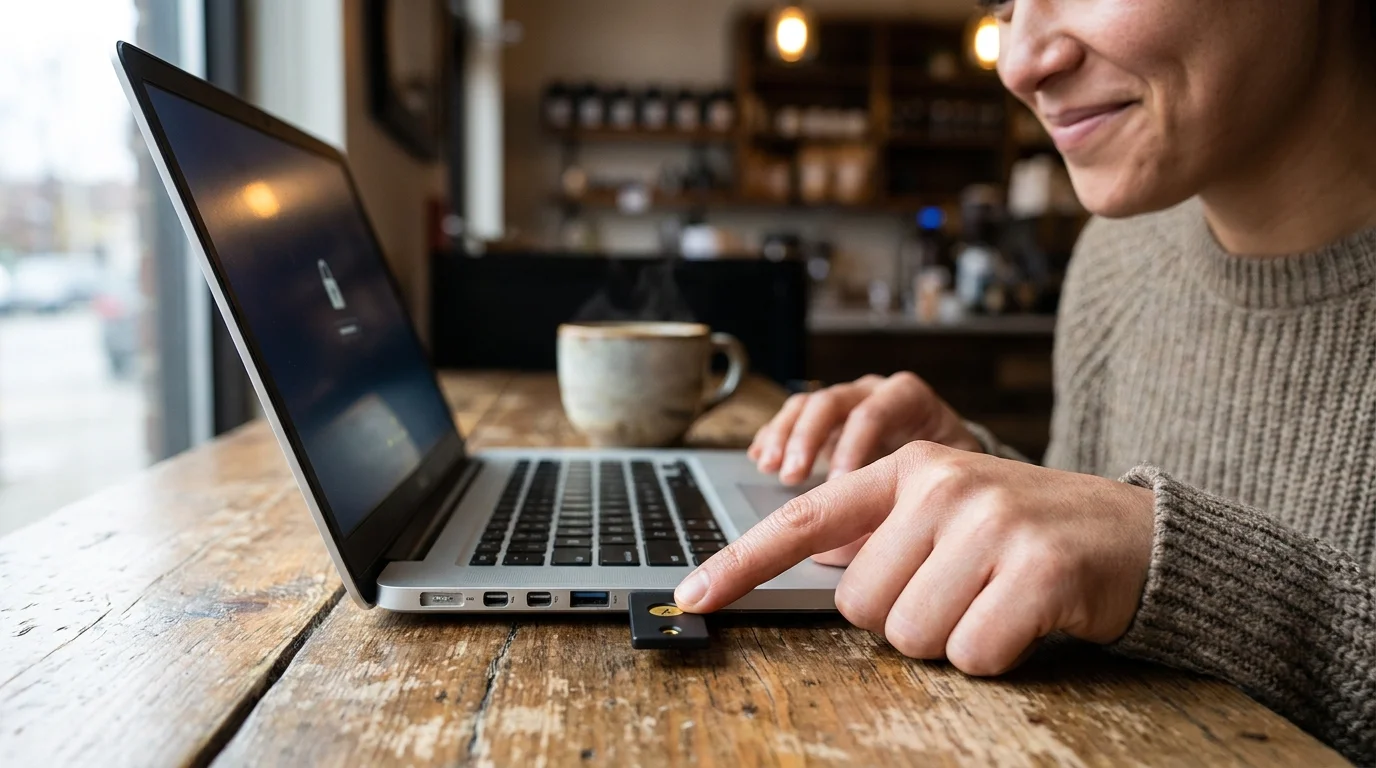
- Select ‘Two-Factor Authentication’ and register your primary hardware key by inserting it and touching the gold contact pad.
- Immediately register your secondary backup key using the identical prompt to guarantee redundant access.
- Crucially, scroll down to your saved phone numbers and toggle off SMS verification as an allowed fallback method.
- Repeat this exact procedure for your password manager, your primary brokerage, and your primary checking account.
The Tactical Toolkit:
- Hardware Standard: FIDO2, WebAuthn, U2F certified.
- Connection Interface: USB-C and NFC dual-compatibility.
- Pairing Redundancy: Exactly two physical keys (Primary Key + Cold Storage Backup).
- Setup Duration: Roughly 8 minutes per critical account.
The Bigger Picture: Reclaiming Your Sovereignty
The modern internet has slowly trained us to accept chronic background anxiety as an unavoidable toll of staying connected. We receive unsolicited verification pings in the dead of night, brace for corporate data breach headlines, and silently wonder whether our mobile carriers truly care about our private affairs. They do not; telecommunications giants are built to move massive volumes of voice and data, not to safeguard human autonomy against organized credential rings.
Transitioning to physical cryptographic keys is more than a technical upgrade; it is a declaration of personal boundaries. When authentication requires your literal hand to touch a physical instrument resting on your desk, you reclaim your perimeter from indifferent telecom providers and nameless attackers across the globe. You sleep soundly knowing that even if the entire cellular network falters, your identity remains anchored precisely where it belongs: in your pocket, in your hands, and completely under your control.
The single greatest vulnerability in modern digital security is trusting a stranger at a telecom desk to guard the gates to your family’s financial life.
| Key Point | Detail | Added Value for the Reader |
|---|---|---|
| Authentication Medium | Physical cryptographic chip (FIDO2/WebAuthn) vs. cellular carrier SMS transmission. | Completely eliminates carrier employee bribery and social engineering risks. |
| Phishing Immunity | Keys verify the exact browser URL cryptographically before releasing authorization tokens. | Protects you even if you accidentally enter credentials into a spoofed website. |
| Hardware Redundancy | Dual-key protocol (Primary on keychain, secondary stored securely at home). | Ensures permanent account access without relying on weak telephone number resets. |
Frequently Asked Questions
What happens if I lose my primary YubiKey while traveling?
As long as you registered a secondary backup key during initial setup, you simply access your accounts using the spare key kept in your home safe or desk, then remove the lost token from your account dashboard with a single click.Can an attacker clone my hardware key if they temporarily steal it?
No. The private cryptographic keys are burned into the secure element of the device during manufacturing and cannot be read, copied, or cloned, even with sophisticated hardware analysis tools.Why isn’t an authenticator app (like Google Authenticator) enough protection?
While software apps are significantly safer than SMS codes, they remain vulnerable to sophisticated reverse-proxy phishing attacks that trick you into typing the live six-digit code into a fake website. Hardware keys verify the actual web domain automatically.Do I need to plug the key into my smartphone every time I check my accounts?
No. You only authenticate when signing into a new device, resetting a credential, or logging into high-security portals. Daily mobile apps remain unlocked via your biometric fingerprint or face scan.What if an online service does not support physical hardware keys?
For services that still lack WebAuthn support, use an app-based TOTP code stored inside your hardware key’s companion software rather than linking your real cellular telephone number.