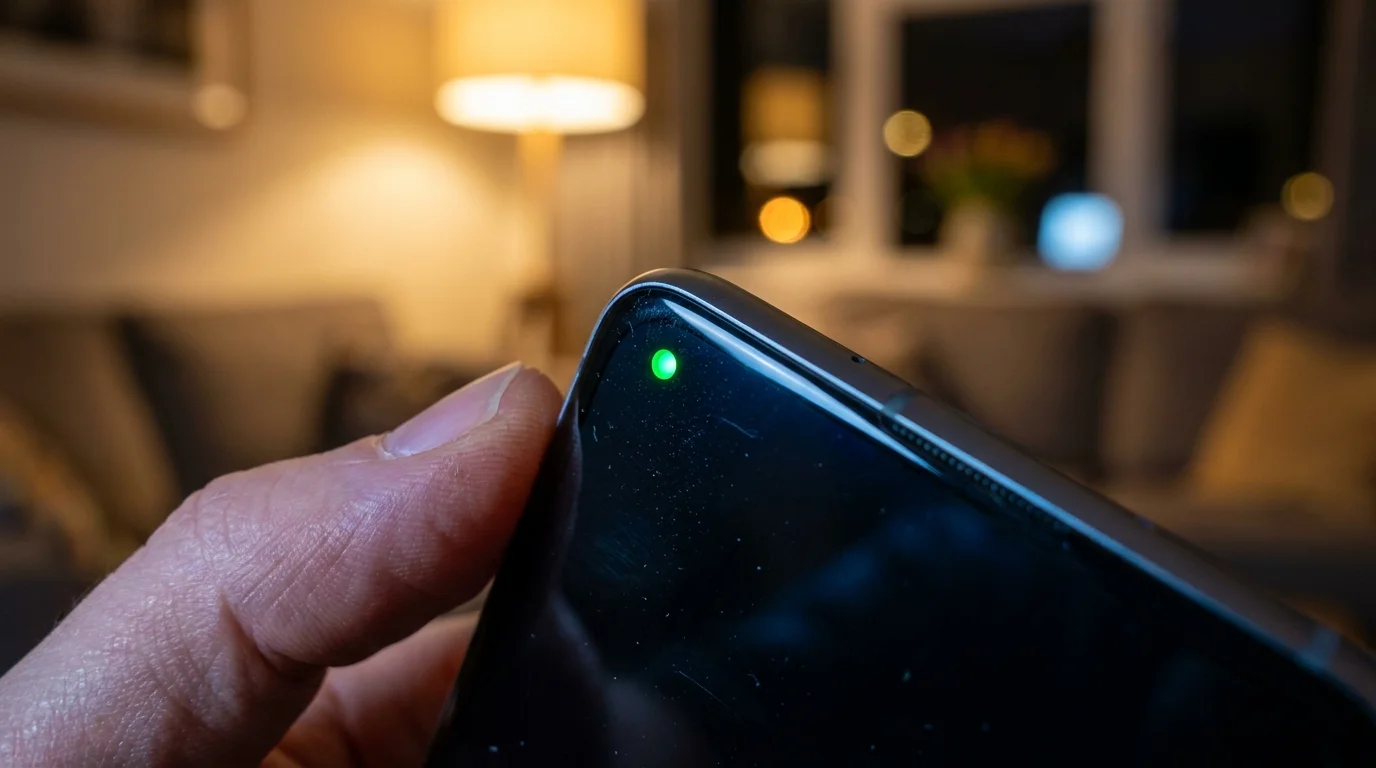
The room is dark except for the amber cast of a bedside lamp. You set your glass of water on the nightstand, prop your phone against a paperback book, and lean back against the pillows. Then, out of the corner of your eye, a needle-sharp pinprick of emerald green pulses in the top corner of your screen. It flares for half a breath, disappears, and leaves you staring at cold glass in the silence.
You did not launch a live stream. You did not open the story shutter to snap a photo of your dog. Yet that tiny green hardware indicator flashed anyway, telegraphing an unsettling reality: the optical sensor on your device just woke up, gathered environmental light, and went back to sleep without your consent.
Most people brush this off as an operating system hiccup or an innocent graphic glitch. But what you are witnessing on Instagram mobile apps is not an optical illusion. It is the real-world fingerprint of automated background privilege re-assignment, a process that quietly reactivates your camera and microphone during silent, overnight package updates.
The Ghost in the Sandbox: Why Permissions Never Truly Sleep
Modern mobile operating systems sell you the comfort of a walled garden. You assume that revoking camera access once turns the glass eye into a decorative piece of dead obsidian. In reality, permission management functions far more like a swinging screen door that unlatches whenever the software rebuilds its internal cache during an update.
When Meta pushes an incremental patch through the Play Store or App Store, the package installer restructures permission flags. By packaging fresh camera-dependent features—like augmented reality reels, automated caption filters, or updated facial tracking—into the app bundle, the software triggers an ambient sensor check upon boot. The device checks optical calibration to confirm lens availability, producing that startling, rhythmic green dot that catches you unawares.
Rather than an aggressive spy operation run by a lone bad actor, this behavior represents corporate telemetry run wild. The application treats your physical sensors not as private hardware owned by you, but as continuous data pipes waiting to be queried whenever the host software re-indexes its dependencies.
- Google Pixel 9 haptics trigger phantom pocket buzzes against resting leg muscles
- Lenovo Legion laptops cap peak processing speeds to mask scorching surface heat
- Frontier Internet outages sever fiber connections leaving thousands offline across southern states
- iPhone 13 batteries restore drained power bars halting costly new flagship upgrades
- DaVinci Resolve tools strip choppy timeline stutter rivaling thousand-dollar video editing suites
The Observation Desk: What a Systems Architect Discovered at Midnight
Marcus Vance, a thirty-nine-year-old network reliability engineer based in Austin, noticed the emerald flash while reviewing server diagnostic logs late one Tuesday evening. His phone sat untouched on an anti-static mat beside his workstation, running network traffic analyzers. Vance watched the green indicator blink three times over forty minutes, perfectly synchronized with silent outbound telemetry pings directed at edge servers in Ashburn, Virginia.
When Marcus inspected the application manifest files post-update, he discovered that an automated maintenance patch had quietly flipped his carefully selected permission state from ‘Ask Every Time’ back to ‘Allow While Using App.’ Because the social media client maintained persistent background app refresh privileges, the phone interpreted idle memory cycles as active usage, allowing the optical stack to initialize and probe the camera sensor without a visible screen prompt.
Audit Layers: Mapping Your Sensor Exposure
Every person engages with social platforms differently, which means your exposure to phantom sensor activation depends heavily on how you carry and store your device throughout the day.
For the Passive Scroller
If you consume media without ever posting clips or filming stories, your hardware requirements are simple. You require high-fidelity display processing and stereo playback, nothing more. For this usage style, keeping any active link between the application container and your camera module introduces needless exposure. Revoking hardware permission completely neutralizes background optical initialization without interrupting your feed.
For the Content Creator
If you record spontaneous video and live feeds, severing camera ties entirely creates constant friction. The solution here relies on sandboxed session rules. Rather than granting permanent access, you force the operating system to purge authentication tokens the moment you swipe the app into suspension. This preserves full studio functionality when the interface is open, while cutting the optical circuit the split second you leave.
For the Workplace Professional
If your device sits beside you in boardrooms or home offices where proprietary documents cover your desk, ambient optical polling is an unacceptable risk. The objective for this profile is to strip background telemetry threads entirely, blocking the application from executing background pings that poll room acoustics or light levels during meetings.
Mindful Application: Locking Down the Optical Gateways
Restoring strict boundaries requires less than five minutes of deliberate tactile adjustment. Instead of trusting app-level settings, you will enforce restrictions at the operating system kernel level.
Follow these steps to eliminate rogue camera polling across your daily hardware:
- Open your primary system settings rather than the in-app preference screen.
- Navigate directly to ‘Apps’, select ‘Instagram’, and tap ‘Permissions’.
- Tap ‘Camera’ and switch the toggle from ‘Allow while using app’ to ‘Don’t Allow’ or ‘Ask Every Time’.
- Return to the main application menu and disable ‘Background App Refresh’ or ‘Allow Background Usage’.
- Under advanced privacy settings, turn off ‘Modify System Settings’ to stop silent auto-updates from re-writing permission manifests.
The Tactical Toolkit requires zero third-party software downloads. You need only your native device settings panel, two minutes of quiet attention, and the discipline to verify these toggles once a month following major system updates.
The Bigger Picture: Reclaiming the Physical Perimeter
A smartphone is the most intimate piece of engineering you own. It rests in your pocket, listens from your nightstand, and catches your face in moments of unfiltered vulnerability. Allowing software developers to treat your physical lenses as free telemetry nodes dulls your sense of environmental sovereignty.
When you close these hidden software loopholes, you are not merely clearing a phantom green dot from your notification bar. You are drawing a definitive line between your personal sanctuary and corporate surveillance creep. Taking ownership of your hardware permissions restores peace of mind, transforming an anxious glowing rectangle back into what it was always meant to be: a quiet, obedient tool that works only when summoned.
The single most effective defense against invisible data harvesting is treating every permission toggle as an airlock rather than an open window.
| Key Point | Detail | Added Value for the Reader |
|---|---|---|
| Ghost Permission Creep | Background app bundles reset sensor flags during automated bug fixes and maintenance patches. | Explains why hardware indicators pulse even when you never touched the camera interface. |
| Telemetry Polling | Idle background threads query optical sensor availability to prepare captioning and AR assets. | Identifies the technical reason behind phantom battery drain and unexplained green light blinks. |
| Kernel-Level Lockdown | Disabling permissions through system settings overrides internal app preferences permanently. | Guarantees complete optical privacy without breaking passive media viewing or feed browsing. |
Frequently Asked Questions
Does that blinking green dot mean an employee is actively watching me through my camera?
No. The green dot confirms that a background process has initialized the camera driver. It almost always indicates automated telemetry polling or asset pre-loading rather than a live human viewer.Why does Instagram need camera access if I only browse the feed?
It does not. The app requests blanket permissions during setup to make story creation frictionless, but you can safely revoke camera and microphone access without losing the ability to view, like, or read posts.Will revoking camera permissions delete my saved drafts or archive?
Not at all. Your account data, drafts, messages, and uploaded photos remain completely intact on the platform servers. Only real-time hardware recording inside the native app is paused.How often do mobile apps silently reset these access privileges?
Privilege resets generally happen during major framework updates or when an app gets uninstalled and reinstalled from cloud backups. Checking your permissions once a month keeps your settings intact.Can third-party privacy apps stop this automatic re-enabling for me?
Native operating system controls are vastly safer and more effective. Third-party permission managers often require intrusive accessibility privileges of their own, creating another privacy risk.