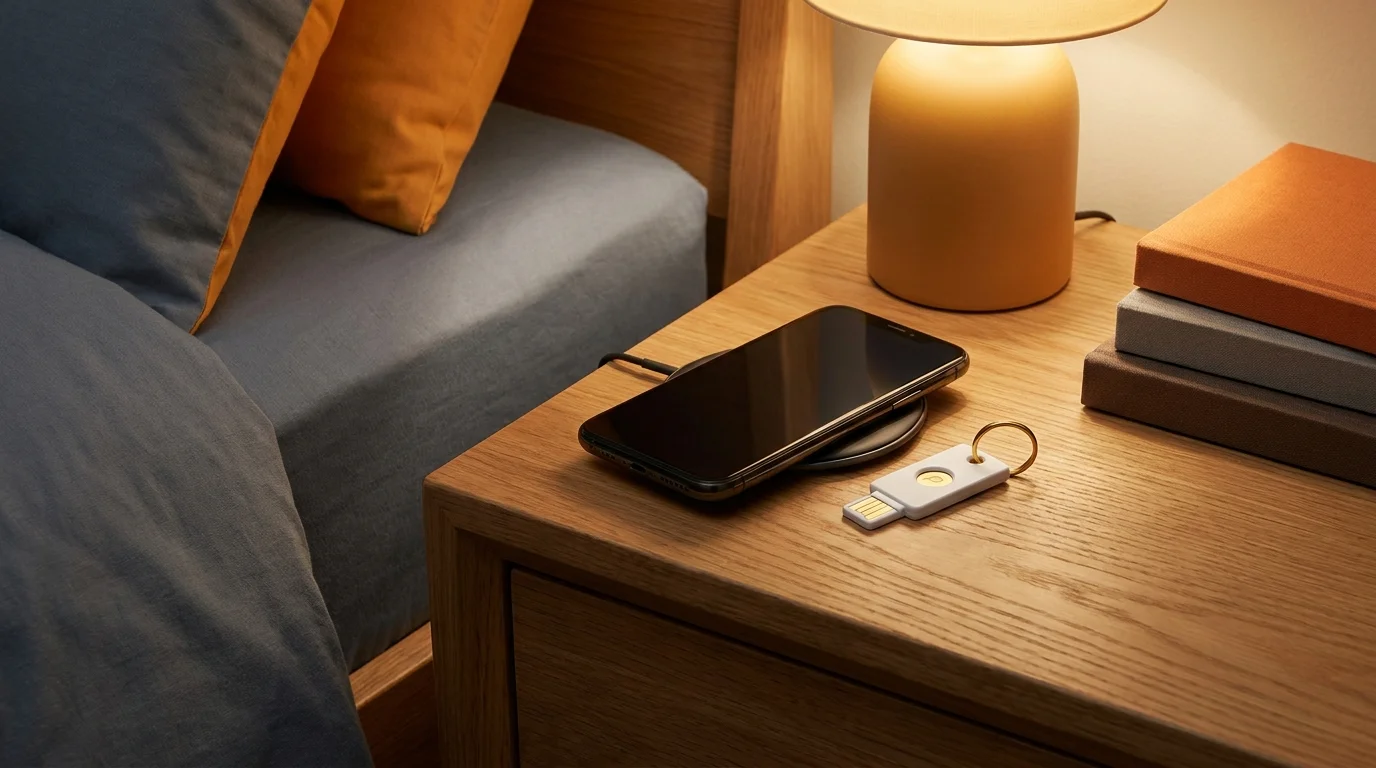
The sudden quiet is what catches you off guard. You are sitting at the kitchen table, morning mug warming your palms, when your phone drops from four bars of cellular signal down to a stark, blank zero. You assume a neighborhood fiber line got cut, or perhaps a routine cell tower reset is underway. But within two minutes, your screen remains eerily mute while notifications should be chiming in.
You glance down at the glass slab, watching the word No Service quietly replace your carrier name. In that exact moment, fifty miles away in a bustling retail strip mall or across the continent in a darkened room, someone you have never met just convinced a hurried store representative that they were you. Your phone number—the single digital thread tethered to your bank accounts, primary email, and personal life—just migrated to a fresh plastic chip resting in a criminal’s burner phone.
We have been conditioned to treat text message verification codes like ironclad deadbolts. Every modern bank, utility provider, and social platform nudges you to link your mobile number for safety. Yet that green text bubble is not a secure lock; it is an open postcard dropped into an unlocked mailbox. The second your mobile signal vanishes, the attacker does not need your password. They simply click ‘Forgot Password’ on your primary account, catch the incoming six-digit text code, and lock you out of your digital existence in thirty seconds flat.
The Digital Postcard: Why Carrier Towers Betray Your Trust
To understand why SMS authentication collapses so easily, imagine trusting your front door key to a casual delivery courier who hands it over to anyone wearing your jacket. Mobile carriers operate on convenience, customer service speed, and human empathy. A rogue worker bribed on Telegram, or a tired retail clerk manipulated by a forged driver’s license, can reassign your number in three keystrokes without touching your physical device.
This is where hardware tokens shift the entire paradigm of digital survival. A Titan Security Key does not ask for your phone carrier’s permission to verify who you are. It operates like a physical brass key crafted specifically for an unpickable lock. Instead of transmitting an ephemeral code across cellular radio towers where rogue relays and social engineers can intercept it, the hardware key handles the handshake right against your device via physical contacts or short-range near-field magnetic induction.
Even if an attacker tricks your mobile provider, drains your phone reception, and cracks your master password through a database breach, their attack grinds to a dead halt. Unless they physically walk into your kitchen and snatch that small token off your brass keyring, they cannot touch your account.
- Pixel Buds Pro pairing toggles silence crackling audio drops across crowded rooms
- Google Photos backup settings wipe original camera rolls during device switchovers
- Fire TV home screens blast noisy autoplay video ads until users disable background telemetry toggles
- Smartphone DC dimming toggles stop aggressive screen flicker easing strained burning eyes during midnight reading
- Fraud alert robocalls spoof local bank numbers stealing login credentials from panicked smartphone owners
Consider Elena Rostova, a 41-year-old independent financial auditor based in Chicago. Last autumn, Elena watched her smartphone lose service while she was reviewing tax records at her desk. Within four minutes, notifications flashed across her laptop alerting her that someone was requesting password resets across her primary Google Workspace and exchange profiles. Because Elena had bound her accounts strictly to a pair of Google Titan keys and stripped away phone recovery, the automated intruder hit a digital brick wall. The scammer had her phone number, her social security digits, and her home address, yet walked away with absolute zero access to her clients’ sensitive balance sheets.
Layering Your Defense: The Three Device Profiles
Securing your life against remote SIM swaps requires recognizing how your daily tech footprint differs from your neighbor’s. Not everyone moves through the world with identical risk exposure.
For the Mobile Nomad and Remote Professional
If your office lives inside a backpack and you routinely work from airport lounges, hotel lobbies, and rented desks, you are in the high-exposure tier. Cellular interception, public hotspot snooping, and opportunistic credential stuffing are daily realities. For this setup, keep a USB-C and NFC-capable Titan key permanently slotted onto your key carabiner. Configure your core email and cloud infrastructure to require hardware tokens, and deliberately strip SMS phone recovery from your backup settings.
When you sign into a new machine on the road, physical contact validates your identity within a fraction of a second. You tap the key against the back of your phone or plug it into your laptop’s side port, press the gold capacitive disc, and carry on without waiting for a text message that might never safely arrive.
For the Minimalist Everyday User
If you rarely switch devices and primarily use your computer for household budgeting, family photos, and online shopping, your goal is quiet friction-free defense. You do not need to carry a key everywhere you walk. Instead, register two identical keys: keep the primary key in your desk drawer next to your computer, and place the second key inside a fireproof lockbox or safe as an emergency spare.
Once configured, you will rarely need to touch the keys during routine browsing on your trusted personal devices. They remain passive until a new login attempt occurs from an unrecognized browser, standing as an invisible guard dog that only barks when an intruder tries entering your perimeter.
Mindful Implementation: Building Your Master Account Fortress
Transitioning away from brittle text verification is a calm, deliberate ritual. Set aside twenty minutes on a quiet weekend morning with a hot cup of tea to complete these steps without distraction.
Never rely on a single hardware key. If you misplace one key without setting up a backup, you risk locking yourself out of your own digital kingdom. Always register hardware authenticators in pairs.
- Pair your keys together: Label one key ‘Daily’ with a tiny dot of metallic paint and mark the second ‘Vault’. Plug the primary key into your laptop and register it through your Google Account security dashboard under the Advanced Protection Program or standard 2-Step Verification menu.
- Register your fallback token immediately: Without closing your browser session, repeat the registration flow with your backup key. Test both keys on an incognito browser window before moving to the next phase.
- Sever the phone number fallback: This is the crucial step most users skip. Scroll down to your verification methods and explicitly remove your mobile number as an authentication pathway. If your account permits SMS fallback, a SIM swap attacker can simply bypass your hardware key by selecting ‘Try another way’.
- Store emergency recovery codes: Print your ten one-time backup codes onto paper. Place this paper alongside your spare key in your physical vault; do not store these numbers as an unencrypted screenshot in your cloud photos.
Your tactical toolkit requires simple essentials: two Titan Security Keys (one USB-C/NFC model and one USB-A/NFC model if you mix port generations), a fine-tip permanent marker for labeling, and fifteen minutes of uninterrupted focus.
The Bigger Picture: Reclaiming Autonomy in an Insecure World
There is a distinct psychological lightness that comes from knowing your digital safety does not rely on a twenty-dollar-an-hour carrier employee working under retail quotas. For over a decade, consumer technology companies pushed us toward frictionless convenience, quietly trading away real resilience in exchange for speed.
Holding a small, cold piece of molded polycarbonate and gold contacts in your hand restores an ancient human dynamic. You lock your house with a physical cylinder; you protect your vehicle with a metal transponder. Securing your digital identity with a physical key brings that same intuitive certainty back into your hands. Your mobile carrier can glitch, towers can drop, and text messages can be intercepted mid-air, but your sanctuary remains yours alone.
Real digital security is not about remembering complex phrases; it is about anchoring your identity to something you can hold in your hand.
| Key Point | Detail | Added Value for the Reader |
|---|---|---|
| SMS Authentication Vulnerability | Relies on cellular routing and human customer service agents vulnerable to social engineering. | Identifies why carrier text verification fails long before a hacker touches your computer. |
| FIDO2/WebAuthn Protocol | Cryptographic public-private key pairing processed locally on hardware chips. | Immune to remote phishing sites because keys only authenticate against genuine domain URLs. |
| Titan Hardware Resilience | Engineered with tamper-resistant firmware developed to prevent physical chip extraction. | Ensures state-sponsored or sophisticated criminal extraction tools cannot clone your physical device. |
Frequently Asked Questions
What happens if I lose my primary Titan Security Key while traveling?
As long as you enrolled a secondary backup key during initial setup, you can access your accounts using the spare stored safely at home. Once logged in, simply revoke the lost key from your security dashboard so it becomes permanently useless to anyone who finds it.Can I still use my mobile banking apps without SMS codes?
Yes. Most progressive financial institutions now allow you to authenticate new logins using authenticator apps, biometric prompts, or direct hardware security keys, letting you disable SMS one-time passcodes completely.Does a hardware key drain my smartphone battery when left plugged in?
No. Titan keys use minimal passive power only during the split-second authentication window when you tap the NFC sensor or press the capacitive contact disc on a USB port.What is the difference between a Titan Key and an authenticator app?
While authenticator apps are significantly safer than SMS, they can still be defeated by sophisticated real-time phishing proxies that trick you into typing the six-digit code. Hardware keys communicate directly with genuine browser domains, making proxy phishing technically impossible.Do I need to carry my hardware key to the gym or grocery store?
No. Once your daily smartphone is authenticated, it stays trusted until you log out, reset the device, or perform sensitive profile modifications, meaning your keys can remain at home during everyday errands.